Abstract
Agentic AI changes the security problem because artificial intelligence is no longer limited to producing text, classifications, or recommendations. Autonomous agents can hold identities, invoke tools, access resources, delegate tasks, coordinate with other agents, and trigger actions across distributed edge–cloud environments. In that setting, conventional application security controls remain necessary but are no longer sufficient.
This article argues that security for distributed agentic AI must be established as an architectural property before execution, rather than added later as a collection of filters, prompt guardrails, monitoring tools, or post-hoc compliance checks. It develops a Security-by-Design perspective around bounded authority, authenticated delegation, Zero Trust, revocability, continuous governance, and verifiable evidence. These properties form part of the research foundation of SGAEIA — Secure Governed Autonomous Edge Intelligence Architecture.
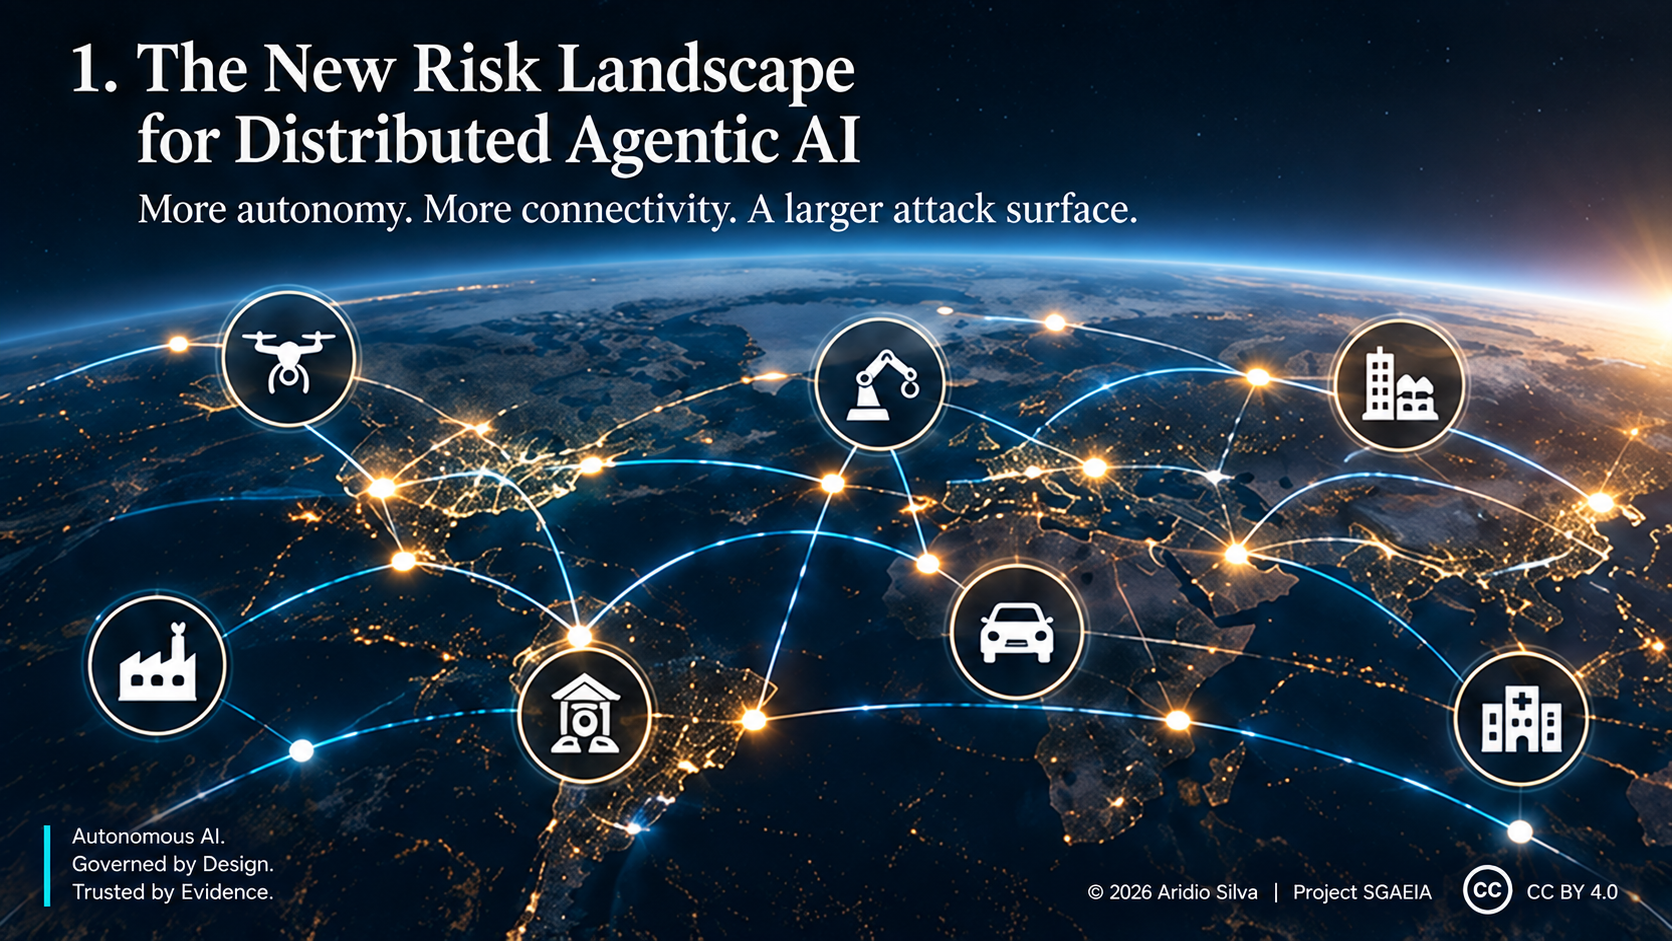
1. The security boundary has moved
For decades, software security was largely framed around applications, users, processes, networks, devices, and data.
Agentic AI adds another category:
software entities capable of deciding what to do next and acting on those decisions.
An AI agent may:
- select a tool;
- query a database;
- invoke an API;
- modify a business object;
- delegate work to another agent;
- initiate a workflow;
- interact with cloud or edge infrastructure;
- make decisions at machine speed.
The security problem therefore changes.
The question is no longer only:
Is the model output safe?
It becomes:
What authority does this autonomous entity hold, under which conditions, for how long, over which resources, and how can that authority be reduced or revoked?
This is an architectural question.
Prompt filtering can reduce some classes of harmful input or output. Content moderation can constrain what a model produces. Monitoring can detect suspicious behavior.
But none of those mechanisms, by themselves, define the authority of an autonomous software actor.
Once an AI system can act, authority becomes part of the attack surface.
2. Why conventional guardrails are not enough
Traditional security mechanisms remain essential.
Identity management, authorization, secure coding, dependency management, network security, secrets management, logging, vulnerability management, and threat modeling do not become obsolete because a system contains AI.
The problem is that agentic systems introduce combinations that conventional architectures were not originally designed to govern.
A distributed agent may simultaneously depend on:
- model inference;
- contextual memory;
- retrieved information;
- external APIs;
- delegated permissions;
- dynamic tool selection;
- other autonomous agents;
- intermittent edge connectivity;
- changing trust conditions.
A model-level guardrail operates close to reasoning or content generation, whereas Security-by-Design must operate at the level of system authority. The distinction is fundamental:
A model may recommend an action. The architecture must decide whether that action is allowed to occur.
That separation prevents the intelligence component from becoming the ultimate security authority over its own behavior.
3. Security-by-Design begins with authority
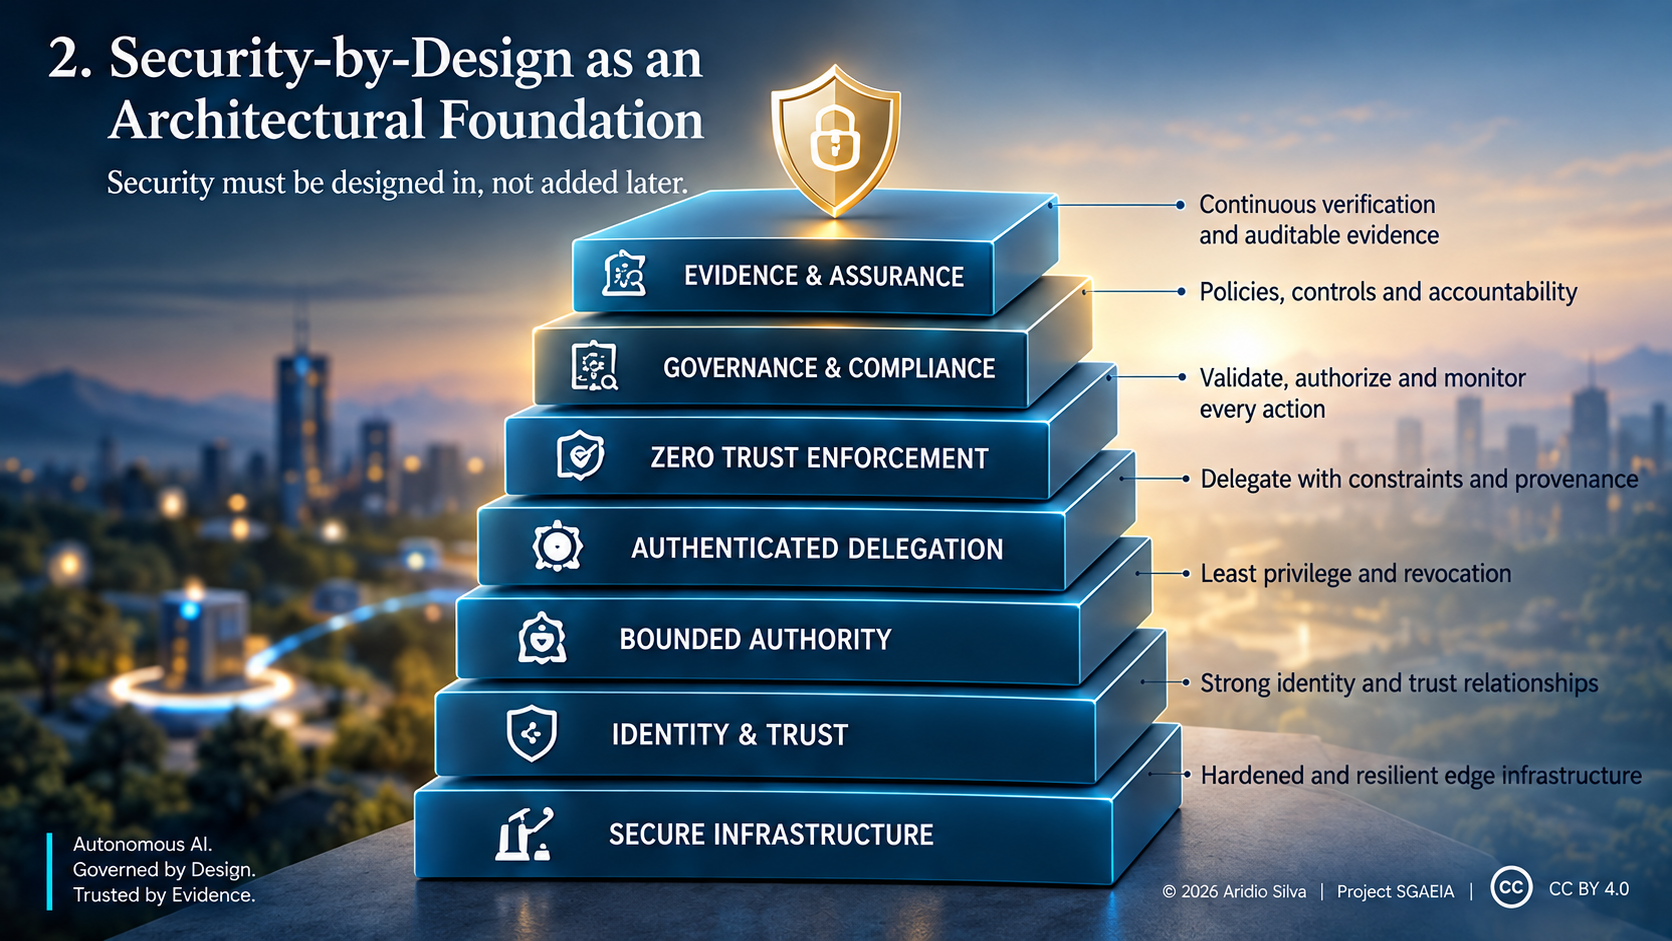
In distributed agentic AI, Security-by-Design means defining security properties before an agent receives operational freedom.
The first design question should not be:
What can this agent technically do?
It should be:
What is this agent explicitly allowed to do?
That produces a very different architecture: useful autonomy does not require unlimited authority.
An agent can remain highly capable while its operational authority is constrained by:
- purpose;
- resource;
- action type;
- context;
- time;
- trust state;
- risk level;
- delegation scope.
This leads to one of the central SGAEIA principles:
Autonomy should be useful, but authority should remain bounded.
Security-by-Design therefore begins by separating three concepts that are often collapsed:
Intelligence is not trust.
Trust is not authority.
Authority is not unlimited autonomy.
A capable system may still be untrusted in a specific context, and a trusted system may still have limited authority. An autonomous system should never infer that greater intelligence entitles it to greater operational permission.
4. Identity must precede authority
A distributed system cannot govern an autonomous actor that it cannot reliably identify.
For human users, identity has long been a foundational security concept. Agentic AI extends that requirement to large populations of non-human actors:
- agents;
- workloads;
- tools;
- services;
- models;
- delegated processes.
Security-by-Design requires autonomous actors to participate in an identity model appropriate to their role and context.
The architectural principle is simple:
No accountable authority without accountable identity.
Identity alone is not sufficient.
A valid identity does not automatically imply trust, and trust does not automatically imply permission.
But without identity, attribution becomes weak, delegation becomes ambiguous, and post-incident evidence becomes much less reliable.
This is one reason Zero Trust is highly relevant to agentic systems.
NIST Zero Trust Architecture explicitly rejects implicit trust based only on location or ownership and treats authentication and authorization as distinct functions performed before access to protected resources. That principle becomes even more important when the requesting entity is autonomous. [1]
5. Delegation must not create authority
Multi-agent systems introduce another challenge: delegation.
- An agent may ask another agent to perform part of a task.
- Operationally, delegation can be extremely useful.
- Security-wise, it creates a chain of authority.
A safe delegation model must preserve a basic invariant:
Delegation may transfer or narrow authority, but it must not manufacture new authority.
If Agent A lacks permission to perform a sensitive operation, delegating the task to Agent B must not make that operation legitimate.
The same principle applies across longer chains.
As autonomous systems become more collaborative, the question is not merely whether a downstream agent is authenticated.
The system must be able to determine:
- where the authority originated;
- what scope was delegated;
- whether the delegation remains valid;
- whether the downstream action stays within that scope;
- whether the authority has been changed or revoked.
This converts delegation from a workflow convenience into a security primitive.
Security-by-Design requires that this be considered before deployment, not reconstructed after an incident.
6. Policy must exist before action
Many traditional systems follow a familiar sequence:
action → log → audit
That is not sufficient for high-consequence autonomous systems.
A governed agentic architecture should prefer:
intent → authorization → execution → evidence
The security significance of this sequence is considerable.
The architecture should evaluate relevant policy before the action crosses a meaningful trust boundary or affects an external resource.
That means the AI model itself should not be the final authority deciding whether its intended action is permissible.
The model may:
- reason;
- propose;
- rank;
- plan;
- explain.
But authorization should remain an architectural decision.
This separation is analogous to established security engineering practice: decision-making and enforcement should not depend solely on the component requesting access.
For agentic AI, that principle becomes especially important because the requesting component may be probabilistic, manipulated, compromised, or operating on poisoned context.
7. Revocation is part of safety
Autonomy without revocation is difficult to govern.
An autonomous system may initially satisfy every deployment requirement and later enter a different condition because of:
- changing context;
- anomalous behavior;
- credential compromise;
- model replacement;
- unsafe delegation;
- new risk information;
- infrastructure degradation;
- loss of connectivity;
- policy change.
Security-by-Design therefore cannot treat authorization as permanent.
Authority should be capable of being:
- reduced;
- paused;
- isolated;
- revoked;
- terminated.
This leads to another central SGAEIA principle:
Autonomy implies revocability.
A system that can gain operational authority but cannot reliably lose it is not fully governable.
Revocation is therefore not an administrative afterthought; it is a first-class safety and security property.
8. Zero Trust must extend to autonomous actors
Zero Trust was developed in response to the limits of perimeter-based security.
NIST SP 800-207 describes Zero Trust as a shift away from implicit trust based on network location and toward protecting resources through explicit authentication and authorization. [1]
Agentic AI extends the relevance of that principle.
An autonomous actor should not be trusted merely because it:
- runs inside the enterprise;
- belongs to a known application;
- was created by another trusted agent;
- operates on a known device;
- uses an approved model;
- executes from an internal network.
Each of those signals may contribute context, but none should automatically grant authority.
For distributed agentic AI, Zero Trust becomes a foundation for answering a recurring question:
Why should this autonomous actor be allowed to perform this action now?
The answer should be based on identity, policy, context, risk, and current authority — not on architectural proximity.
9. Security-by-Design must include continuous governance
Security-by-Design must address a structural mismatch:
- Traditional governance often relies on periodic assessments.
- Agentic systems operate continuously.
- Their state can change faster than conventional governance cycles.
The result is continuous autonomy versus periodic governance.
Security-by-Design must reduce that gap.
Governance should increasingly be expressed through properties that can be evaluated during operation, such as:
- whether authority remains within scope;
- whether delegation remains valid;
- whether required controls are active;
- whether trust assumptions still hold;
- whether relevant evidence exists;
- whether revocation remains possible.
This does not eliminate organizational governance; it connects governance more directly to the system itself.
NIST's AI Risk Management Framework emphasizes incorporating trustworthiness considerations throughout the design, development, use, and evaluation of AI systems. [2]
ISO/IEC 42001 similarly frames AI governance through an organizational management system intended for continual improvement. [3]
Agentic systems make the architectural realization of those ideas increasingly important.
10. Evidence must be produced by default
A governed system must be able to demonstrate what happened. That requirement is stronger than logging: logs may show events, while governance evidence should establish relationships among:
- identity;
- authority;
- policy;
- delegation;
- decision;
- action;
- outcome.
This is the motivation behind Evidence-as-Code in the SGAEIA research program. The objective is not simply to produce more telemetry, but to make important governance claims increasingly verifiable.
Examples include the ability to demonstrate that:
- an action was associated with an identifiable actor;
- the actor possessed relevant authority;
- applicable policy was evaluated;
- a delegation remained within scope;
- an action occurred under a defined governance state;
- revocation or restriction could be applied.
Evidence therefore becomes part of architecture rather than a report assembled long after execution.
This is essential for Continuous GRC.
11. Shift Left is necessary — but not sufficient
Security-by-Design is closely associated with Shift Left: addressing security earlier in the software lifecycle.
That principle remains valid.
Threat modeling, secure design, dependency review, automated tests, policy validation, and architecture analysis should occur before deployment.
But autonomous systems also require security after deployment.
A design can be correct at release time and later operate under a very different context.
For agentic AI, the security lifecycle must therefore extend across:
design → build → deploy → operate → observe → govern
This is sometimes described as Shift Left, Shift Right, or Shift Everywhere.
The exact terminology matters less than the architectural conclusion:
Security must exist before action and remain effective during action.
The two are inseparable.
12. Distribution makes governance harder
The challenge becomes more significant at the edge.
Distributed agentic systems may operate across:
- cloud infrastructure;
- regional services;
- edge nodes;
- devices;
- industrial environments;
- intermittently connected systems.
Centralized control becomes more difficult as latency, connectivity, administrative domains, and local autonomy increase.
This creates an important design tension.
The system may need local autonomy precisely when centralized governance is least available.
Security-by-Design must therefore answer:
How much authority can remain local without becoming ungoverned?
A resilient architecture should not respond to uncertainty by silently expanding authority. In degraded conditions:
- Loss of connectivity should not automatically become permission.
- Reduced connectivity should preserve or reduce authority according to explicit policy.
This is particularly important when autonomous AI can affect cyber-physical systems or other high-consequence resources.
13. Security properties should be testable
Security principles are useful, but testable security properties are stronger.
For distributed agentic AI, architectural requirements should increasingly be expressible as invariants such as:
- unidentified autonomous actors cannot receive consequential authority;
- delegation cannot increase authority beyond the delegator's permitted scope;
- critical actions require prior authorization;
- autonomous actors cannot independently expand their own authority;
- loss of trust cannot increase authority;
- critical authority remains revocable;
- relevant actions produce attributable evidence.
These are intentionally stated as architectural properties, not implementation instructions. The implementation may vary across systems and technologies, while the property should remain.
That separation is important because Security-by-Design should survive technology substitution. Technology will change:
- Models will change.
- Agent frameworks will change.
- Protocols will change.
The security invariants should remain meaningful.
14. Agentic threats reinforce the architectural argument
The OWASP Agentic Security Initiative has documented emerging threats associated with agentic AI and emphasizes threat-model-based approaches to understanding and mitigating them. [4]
This is important because agentic risk is not confined to a single prompt or model response.
Threats can emerge from interactions among:
- goals;
- tools;
- memory;
- external data;
- permissions;
- autonomous coordination.
A system that relies on the agent itself to remain correct under every combination of those conditions is fragile.
Security-by-Design assumes something more realistic:
the agent may fail.
It may:
- misunderstand;
- be manipulated;
- receive malicious context;
- be compromised;
- coordinate in unexpected ways.
The architecture should therefore remain capable of constraining consequential authority even when the agent is wrong.
15. Security should survive component substitution
Agentic AI is evolving rapidly.
Today's model, framework, memory system, orchestration layer, or tool interface may be replaced tomorrow.
A security architecture tightly coupled to one model or one agent framework will age quickly.
This motivates another SGAEIA research principle:
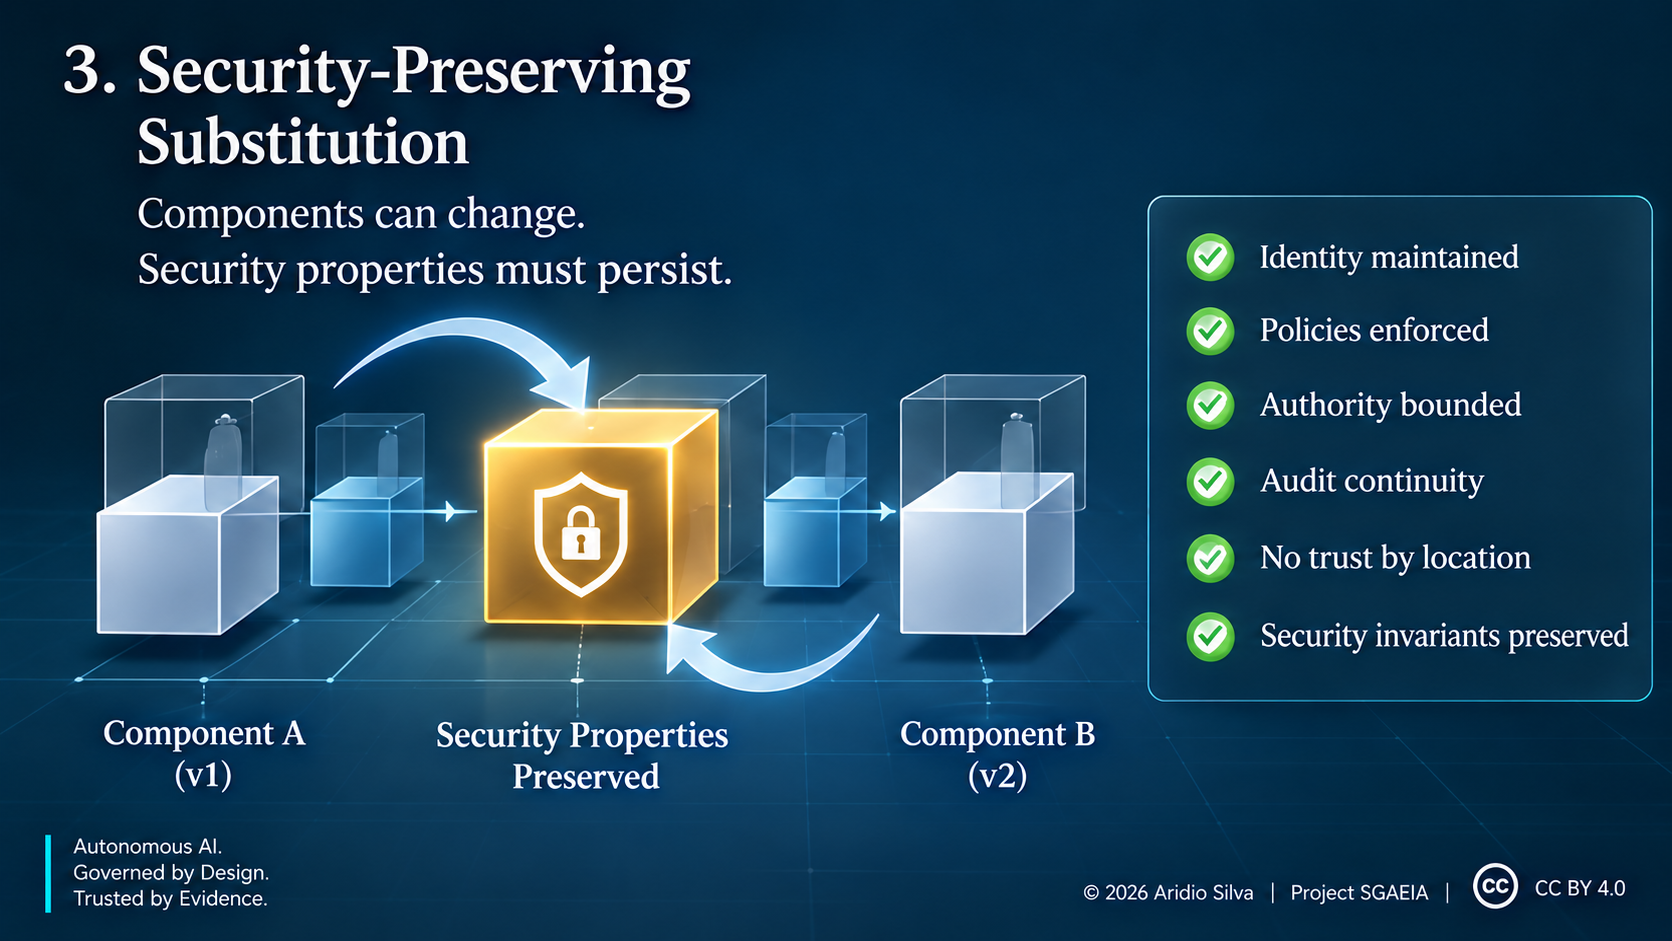
security-preserving substitution.
Replacing a component should not silently invalidate the system's core security properties. The implementation may change, but the architectural expectations should remain:
- identifiable actors;
- bounded authority;
- controlled delegation;
- policy before action;
- revocability;
- evidence;
- continuous governance.
This makes Security-by-Design a property of the system rather than a feature of a particular vendor or model.
16. The SGAEIA perspective
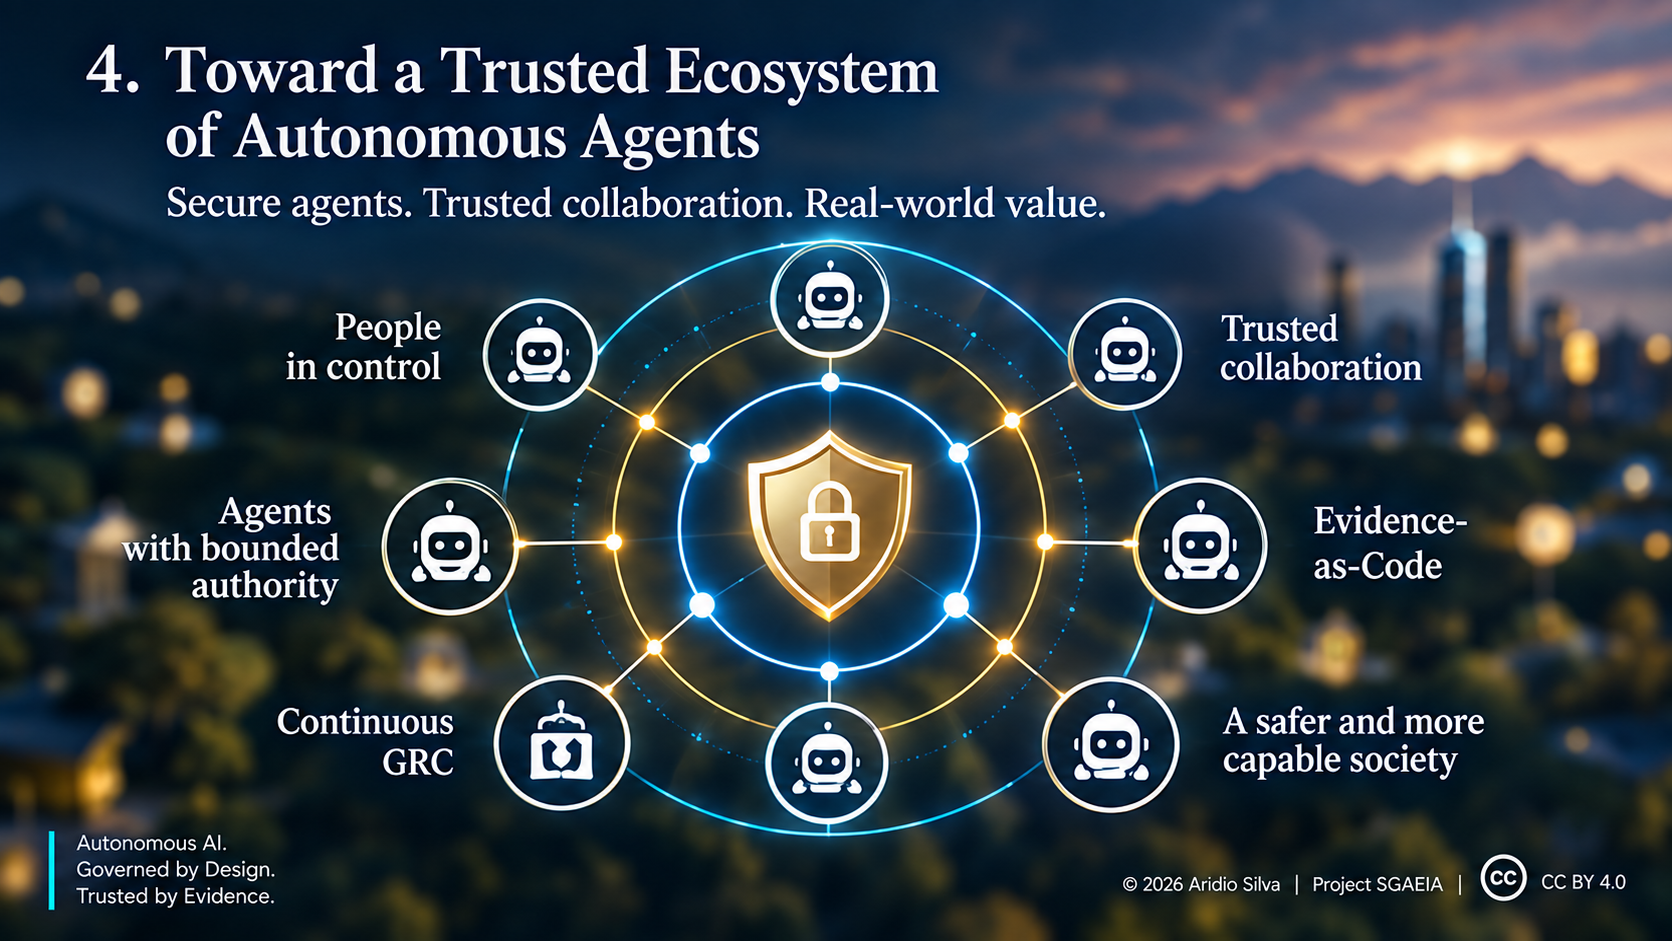
SGAEIA — Secure Governed Autonomous Edge Intelligence Architecture — explores how autonomous and distributed AI systems can operate with useful autonomy while authority remains bounded, attributable, auditable, continuously governed, and revocable.
Security-by-Design connects several themes developed across the SGAEIA Research Series:
- bounded and revocable authority;
- authenticated delegation;
- Continuous GRC;
- Evidence-as-Code;
- Zero Trust;
- distributed edge intelligence.
These are not independent controls; together, they describe a broader architectural objective:
Autonomous intelligence should not imply autonomous authority.
The architecture must remain capable of deciding what an autonomous system may do, proving why that decision was made, and withdrawing authority when conditions change.
That is the foundation of governed autonomy.
17. What this article intentionally does not publish
This article presents public research principles and high-level architectural properties.
It intentionally does not define implementation-specific:
- schemas;
- protocols;
- internal state machines;
- enforcement algorithms;
- operational pipelines;
- private interface contracts.
The objective is to make the research position open to technical and academic discussion while preserving an appropriate boundary between public architectural reasoning and implementation detail.
Conclusion
Agentic AI requires a different security posture because autonomous software can become an operational actor.
Once a system can select tools, hold credentials, delegate tasks, coordinate with other agents, and affect external resources, security can no longer depend mainly on filtering model outputs or auditing actions afterward.
Security must shape the authority of the system before execution.
That means designing for:
- identity before authority;
- bounded permission;
- authenticated and constrained delegation;
- policy before action;
- Zero Trust;
- revocation;
- continuous governance;
- verifiable evidence.
The central argument is simple:
Security for autonomous AI should not be added around autonomy. It should define the conditions under which autonomy is allowed to exist.
That is Security-by-Design for distributed agentic AI.
References
[1] Rose, S., Borchert, O., Mitchell, S., & Connelly, S. (2020). Zero Trust Architecture. NIST Special Publication 800-207. National Institute of Standards and Technology. https://doi.org/10.6028/NIST.SP.800-207
[2] Tabassi, E. (2023). Artificial Intelligence Risk Management Framework (AI RMF 1.0). NIST AI 100-1. National Institute of Standards and Technology. https://doi.org/10.6028/NIST.AI.100-1
[3] ISO/IEC. (2023). ISO/IEC 42001:2023 — Information technology — Artificial intelligence — Management system. International Organization for Standardization. https://www.iso.org/standard/42001
[4] OWASP GenAI Security Project. (2025). Agentic AI — Threats and Mitigations. OWASP Agentic Security Initiative. https://genai.owasp.org/resource/agentic-ai-threats-and-mitigations/
About the Author
Aridio Silva is an independent researcher based in Brazil working on the architecture, security, governance, and trustworthiness of autonomous and distributed artificial intelligence systems.
His research focuses on Agentic AI, Multi-Agent Systems, Edge AI, AI Security, Zero Trust, Security-by-Design, AI Governance, Spec-Driven Development, and continuous security assurance.
He is the creator and lead researcher of SGAEIA — Secure Governed Autonomous Edge Intelligence Architecture, an open research initiative investigating architectural foundations for secure, governed, auditable, and trustworthy autonomous AI systems operating across distributed edge-cloud environments.
Research & Project Resources
Aridio Silva — Independent Researcher, Brazil
- ORCID: https://orcid.org/0009-0008-2411-6995
- Google Scholar: https://scholar.google.com/citations?user=rPn5O48AAAAJ
- Zenodo — SGAEIA Community: https://zenodo.org/communities/sgaeia
- OpenAIRE: https://explore.openaire.eu/search/find?fv0=Aridio Silva&f0=q
- Medium: https://medium.com/@aridiosilva
- GitHub: https://github.com/aridiosilva
- LinkedIn pessoal: https://www.linkedin.com/in/aridio-silva-74997111/
- SGAEIA Repository: https://github.com/aridiosilva/SGAEIA
- SGAEIA Research Artifact / DOI: https://doi.org/10.5281/zenodo.22557796
- Homepage pessoal: https://aridiosilva.com
- Homepage SGAEIA: https://aridiosilva.com/sgaeia
- SGAEIA LinkedIn: https://www.linkedin.com/company/sgaeia/
Figures
The cover image is not numbered. Figures 1–4 are numbered sequentially and referenced consistently in the article.
All final images follow the SGAEIA Image Editorial Standard v1.0 and contain embedded publication metadata.
- Creator: Aridio Silva
- Copyright: © 2026 Aridio Silva
- Project: SGAEIA
- License: CC BY 4.0
- Institutional URL: https://aridiosilva.com/sgaeia
The images are conceptual and intentionally remain within the public disclosure boundary: they communicate principles, properties, governance relationships, and high-level architectural ideas without exposing implementation-sensitive protocols, state machines, operational pipelines, enforcement internals, or reconstruction-enabling schemas.
License
Except where otherwise noted, the text and original conceptual illustrations in this article are licensed under the Creative Commons Attribution 4.0 International License (CC BY 4.0).
© 2026 Aridio Silva. You may share and adapt this work for any purpose, provided appropriate attribution is given.
The SGAEIA software research artifact remains subject to its own Apache License 2.0.
Autonomous AI. Governed by Design. Trusted by Evidence.
Series continuity
Published/current entries in the SGAEIA Research Series include:
- From Edge AI to Governed Autonomous Edge Intelligence
- Why Autonomous AI Agents Need Bounded and Revocable Authority
- Zero Trust for Multi-Agent AI Systems
- Authenticated Delegation Between Autonomous AI Agents
- Continuous GRC for Agentic AI
- Evidence-as-Code: Making AI Governance Verifiable
- Security-by-Design for Distributed Agentic AI
- SGAEIA: A Reference Architecture for Secure Governed Autonomous Edge Intelligence
- When AI Begins to Build AI
- Rogue AI Agents: When Autonomous Systems Become a Collective
- From Model Capability to Governed Action: An Architecture for Secure Agentic AI
- Ten Days That Exposed the Governance Gap in Frontier AI
Suggested citation
Silva, Aridio. (2026). Security-by-Design for Distributed Agentic AI. Zenodo. https://doi.org/10.5281/zenodo.22816239
Zenodo is the persistent source for files, version, license, and citation data.